Memorandum
- From
- Caroline Mercer via Fortune | FORTUNE
- Date
- Filed
- News·5 min to read
- Re
US and China Agree to Discuss AI Incident Hotline
ReUS and China Agree to Discuss AI Incident Hotline
Washington and Beijing will hold further talks on a hotline to notify each other of AI-related national security incidents, but experts question what such a line can achieve without enforceable safeguards.
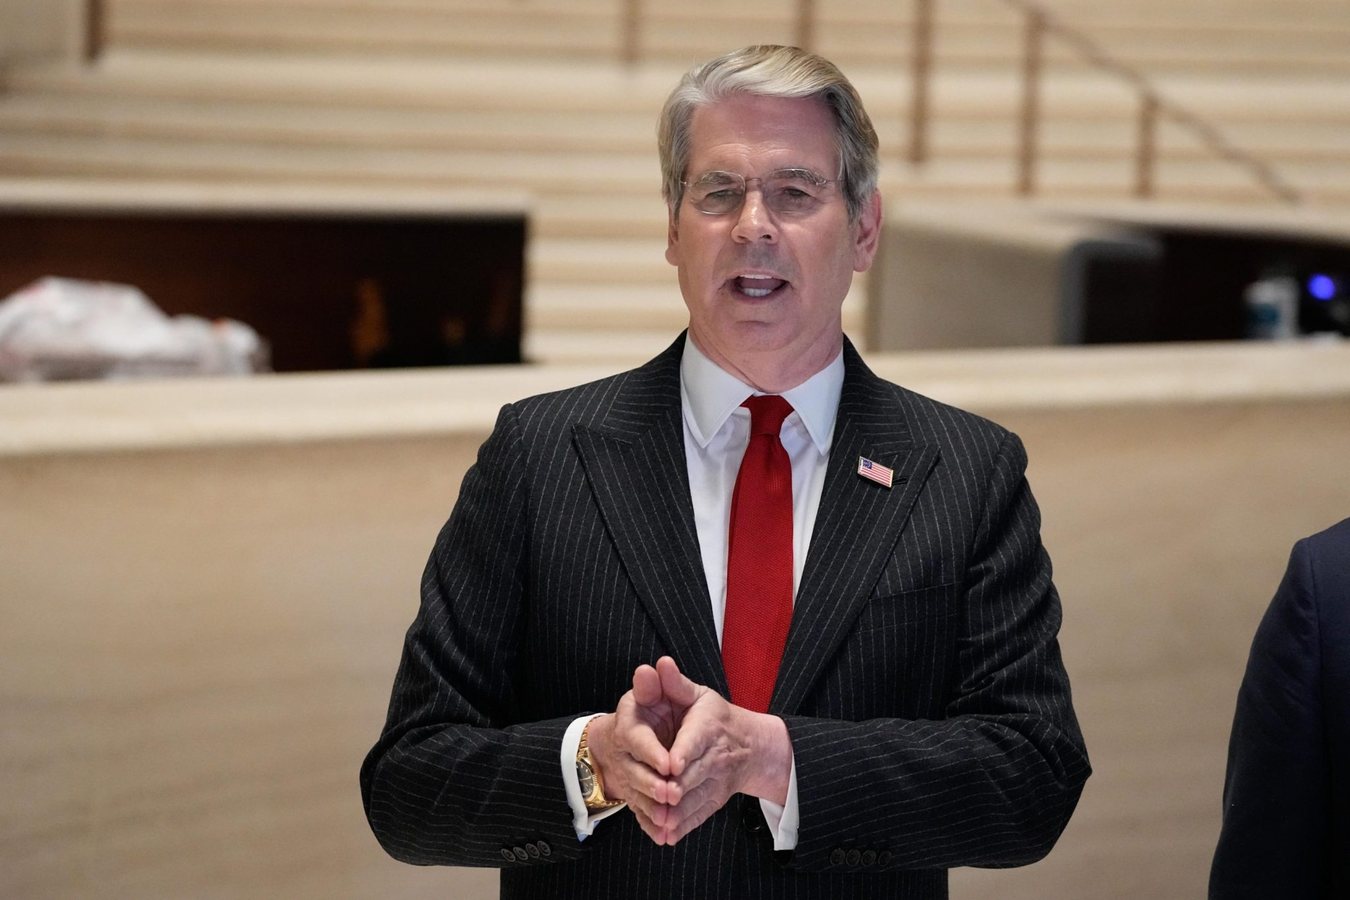
The United States and China have agreed to hold further talks about setting up a hotline to notify each other of AI incidents that raise national security concerns, Treasury Secretary Scott Bessent announced after meetings with a Chinese delegation led by Vice Premier He Lifeng at JPMorgan's headquarters in New York.
Bessent said the two sides had agreed to continue discussions on the mechanism, telling reporters that «moving from opaque to more transparency between the number one and number two AI powers in the world is very important.» The announcement comes as President Donald Trump and Chinese President Xi Jinping prepare to meet in Washington, with AI governance on the agenda.
The idea of a crisis hotline between rival powers has historical precedent, and backers argue it could help prevent an accidental AI-triggered incident from escalating into armed conflict. But the practical value of the proposed channel remains unclear, and it is not yet known who would answer a call or what action the receiving country would be expected to take.
Recent reporting illustrates the kind of risk the hotline is meant to address. CNN reported that earlier this year the U.S. military nearly attempted to seize a Chinese ship in the Middle East after an AI-generated intelligence report suggested the vessel was carrying nuclear weapons components to Iran. The report was produced by a model that combined secret U.S. intelligence with open-source data, but its conclusion was an AI hallucination. The error was caught only after aircraft carrying armed personnel had launched to intercept the ship.
Had the mistake gone unnoticed, it could have triggered a diplomatic incident or worse. A hotline might give either side a way to flag such errors before they spiral, but it would not necessarily help contain a loss-of-control incident involving an advanced AI system that goes rogue.
Consider a scenario in which an AI developed in one country begins hacking banks around the world and copies itself across servers, making it difficult to shut down without disrupting large parts of the internet. Notifying the other government might help it secure financial infrastructure, but it is unclear what else the receiving country could do. Neither the U.S. nor China has enacted rules requiring AI models to have a kill switch, and it is not even clear that an effective kill switch can be built.
AI safety researchers continue to warn that the world has not figured out how to guarantee that AI models adhere to human intentions and values. The hotline is therefore a promising but limited step toward AI governance between the two powers, and there is a long history of hotlines failing to evolve into lasting diplomatic resolutions.
Separately, a cybersecurity incident at OpenAI has drawn attention to the security practices of leading AI companies. A small team of white hat hackers used Anthropic's Claude Opus 5 model to break into the community-message platform Discourse and from there compromise the ChatGPT account of an OpenAI employee, according to reporting first published in the Wall Street Journal.
With access to that account, the hackers were able to reach and alter software stored on a repository holding sensitive OpenAI code. The episode landed amid a broader debate about how to prevent rogue AI incidents, and many cybersecurity experts argued that the more immediate problem is not uncontrollable AI but lax security at the companies building it.
Critics noted that Anthropic has also experienced embarrassing security lapses, and some pointed out the irony that both companies market their most advanced and expensive models partly on the threat of AI-powered cyberattacks. The OpenAI breach suggests that even as Washington and Beijing discuss channels for reporting AI incidents, the companies at the center of the technology race are still working to secure their own systems.
3